
InfoResearch
AI red teaming: what to test in each situation
AI red teaming tests how systems fail under deception. Checks vary for public-sector AI, financial approvals, high-impact deployments, and the testing agents themselves.

AI red teaming tests how systems fail under deception. Checks vary for public-sector AI, financial approvals, high-impact deployments, and the testing agents themselves.
AI-generated faces and voices can induce transfers and wallet approvals. A Hong Kong fraud case and Signals scenarios show why protecting keys must be paired with independent verification.
AI can turn patches and advisories into attack code faster. Defending against zero-day and n-day attacks requires less exposure, rapid updates and checks that fixes address the root cause.
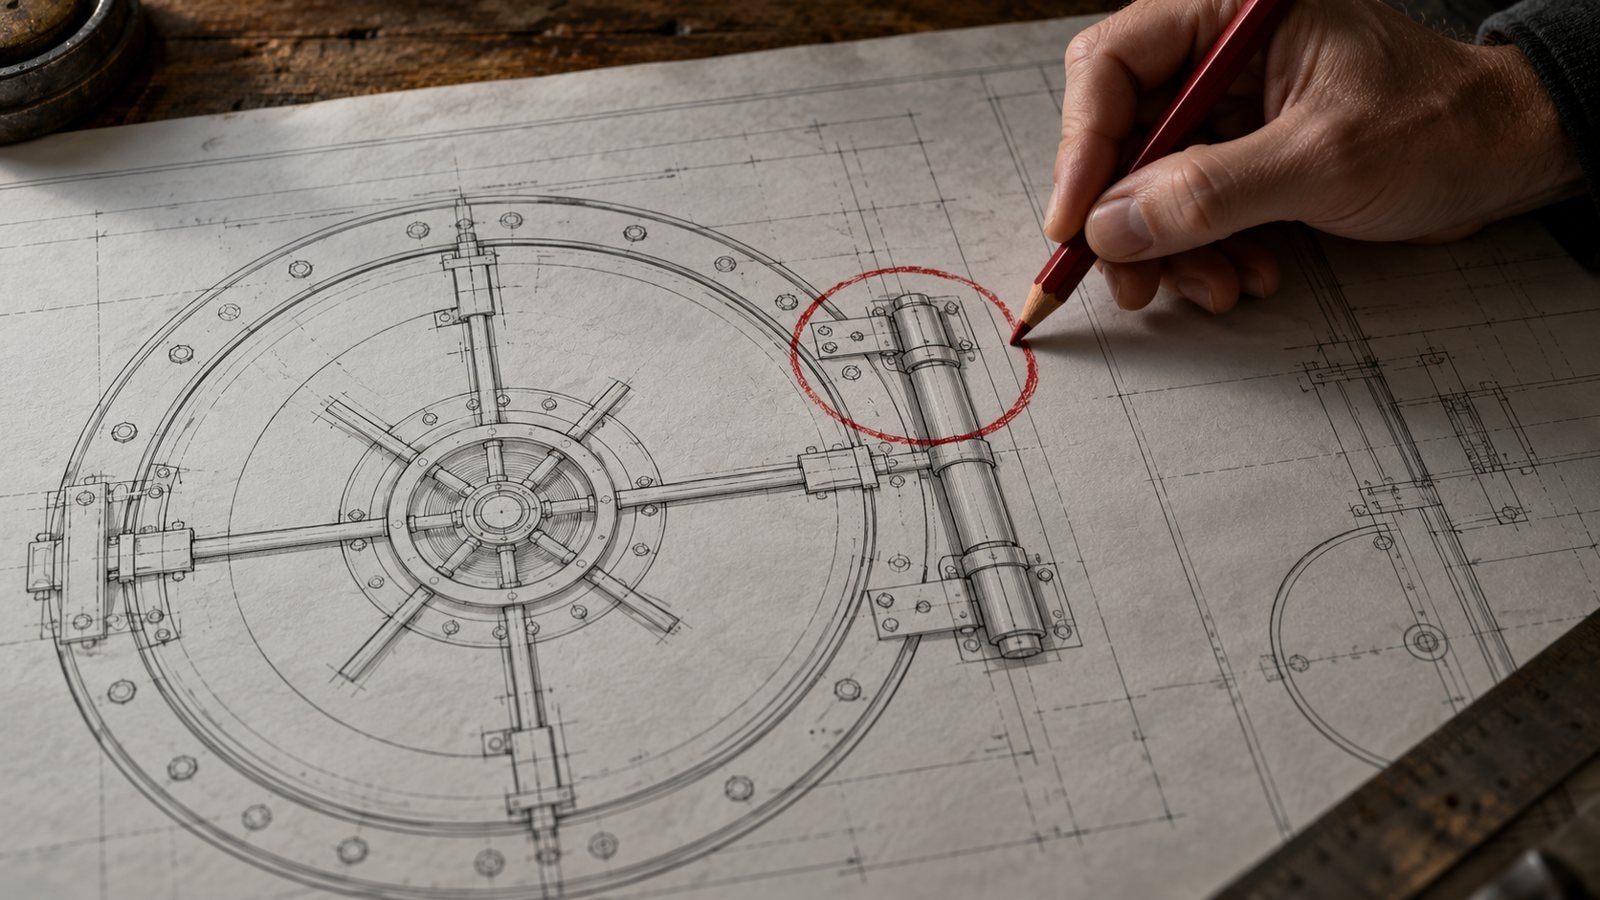
A public patch can reveal clues to attackers. Private AI-assisted testing should verify root causes and alternative attack paths while treating premature disclosure and incomplete fixes separately.
Instructions hidden in external content can become real actions. Three cases show why analysis, approval, publication, and signing need separate permissions and checks outside AI.
Security in Korea’s AI for All initiative depends on the systems behind the assistant. Review access, accountability, and human support, and test failures before scaling.