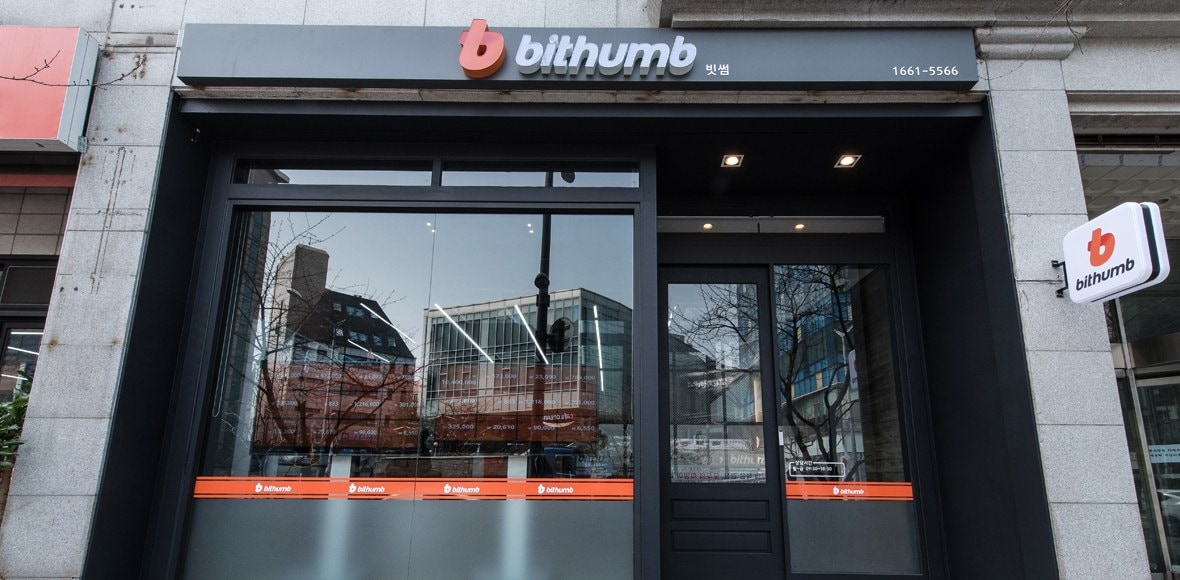
Bithumb confirmed on Oct 27 that an unauthorized outsider had accessed its internal mobile groupware system and personal data had been exposed. The incident was reported on Oct 28. Groupware is used by employees to handle work and share information.
Whether the exposed material includes customer information remains under review. The fact that this was an internal work system does not establish that only employee data was affected. It also does not establish that customer data was exposed.
The specific data fields and the scale of the breach have not been confirmed.
Bithumb said it had reported the incident to the Korea Internet & Security Agency and the Personal Information Protection Commission. The company said it was analyzing the scope of the breach, including the possibility that customer information was involved. The confirmed account does not explain how the outsider obtained access.
As a precaution, open the official app directly to check notices. Verify unexpected messages through official support channels. Avoid suspicious links and attachments, and keep passwords and verification codes private.
Photo: Bithumb